

What HTTP and HTTPS actually are
HTTP stands for HyperText Transfer Protocol. It is the set of rules that governs how data travels between your browser and a web server. When you type a web address and press enter, your browser uses HTTP (or HTTPS) to request a page and receive it back.
HTTPS is HTTP with an added security layer called TLS (Transport Layer Security). TLS encrypts the data moving between your browser and the server, so that even if someone intercepts it on the way, they see scrambled noise instead of readable content. For a plain-language breakdown of how that encryption works, see Encryption Explained Without the Math.
The "S" in HTTPS means the connection is encrypted. That is the entire practical difference between the two protocols for everyday users.
What the padlock icon does and does not mean
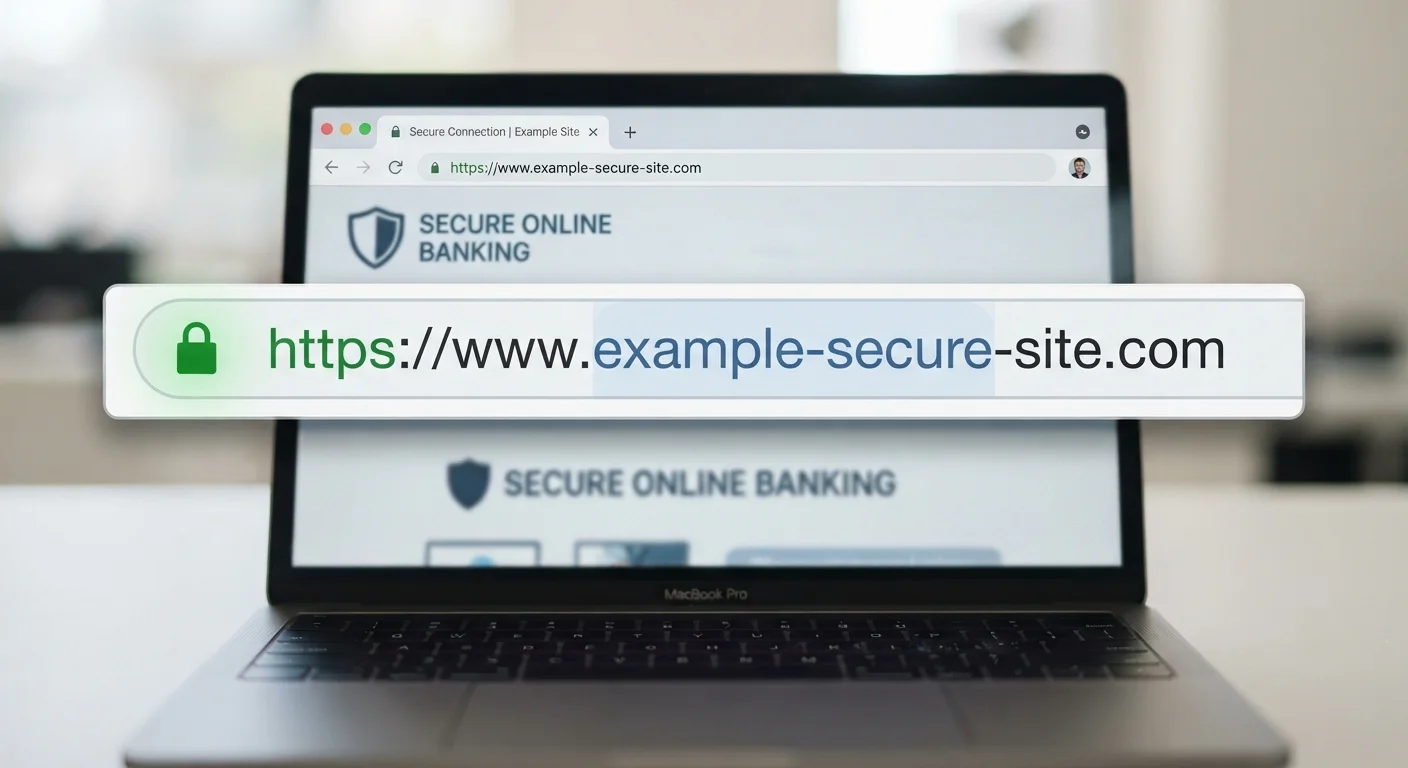
Browsers display a padlock icon in the address bar when a site is using HTTPS. That padlock tells you one specific thing: the data traveling between your device and that server is encrypted. It does not tell you anything about who owns the site, whether the site is honest, or whether your data is safe once it arrives.
A phishing site designed to steal your login credentials can use HTTPS. The padlock will still appear. What HTTPS prevents is a third party on the network, such as someone on the same coffee shop Wi-Fi, from reading the data as it travels. It does not prevent a bad-faith website from misusing the data you willingly submit.
| Criterion | HTTP | HTTPS |
|---|---|---|
| Data encryption in transit | None | Yes, via TLS |
| Padlock shown in browser | No | Yes |
| Protects data on the server | No | No |
| Confirms site is trustworthy | No | No |
| Hides domain from ISP | No | No |
| Browser warning shown | Yes, on major browsers | No |
| Standard for modern websites | No | Yes |
This distinction matters especially when you receive a link by email or text. Before entering any personal information, verify the domain name in the address bar, not just the padlock. For more on what public networks expose, see Public Wi-Fi and Your Data.
Where HTTPS protection starts and stops
TLS encryption protects data in transit. That means the window of protection is the journey from your browser to the web server. Once data arrives at the server, HTTPS has done its job. What the server does with that data afterward is outside HTTPS's scope entirely.
Passwords stored in plaintext on a poorly secured server, personal data sold to third parties, or information exposed in a data breach are all problems HTTPS cannot prevent. This is why using a password manager to generate unique passwords matters even on HTTPS sites. See Password Managers Demystified for how that protection works.
HTTPS also does not hide which website you are visiting. Your internet service provider and network operators can still see the domain (for example, example.com), though not the specific pages or data exchanged. A VPN addresses that layer separately. VPNs: What They Actually Protect Against covers where that tool fits in.
How browsers handle HTTP sites today
Major browsers including Chrome, Firefox, Safari, and Edge now mark HTTP pages with a warning. Chrome labels them "Not secure" in the address bar. When you land on an HTTP login or payment page, most browsers show a more prominent alert.
Search engines also treat HTTPS as a ranking signal, which means HTTP sites are disadvantaged in search results. For website owners, the practical case for switching to HTTPS has become straightforward. Free certificate options through services like Let's Encrypt (a nonprofit certificate authority) removed the main cost barrier years ago.
For users, the browser warning is a reliable prompt to pause before entering any information. If a site asks for a password or payment details over plain HTTP, that is a concrete reason to be cautious. Incognito Mode: What It Does and Does Not Hide explains another commonly misunderstood browser signal.
Certificate warnings are different from "Not secure"
If your browser shows a full-screen warning about a certificate error (rather than just "Not secure"), that is a separate issue. It means the site's HTTPS certificate is expired, misconfigured, or does not match the domain. In that case, the encrypted connection itself cannot be verified. Treat a certificate error as a stronger caution than a plain HTTP warning and avoid entering any personal data until the issue is resolved.


